End Ransomware.
Stop Data Exfiltration.
Block Infostealers.
The kernel-free platform behind ByteJams Ranger: autonomous, on-device detection with no signatures, no cloud dependency, and no performance tradeoffs.
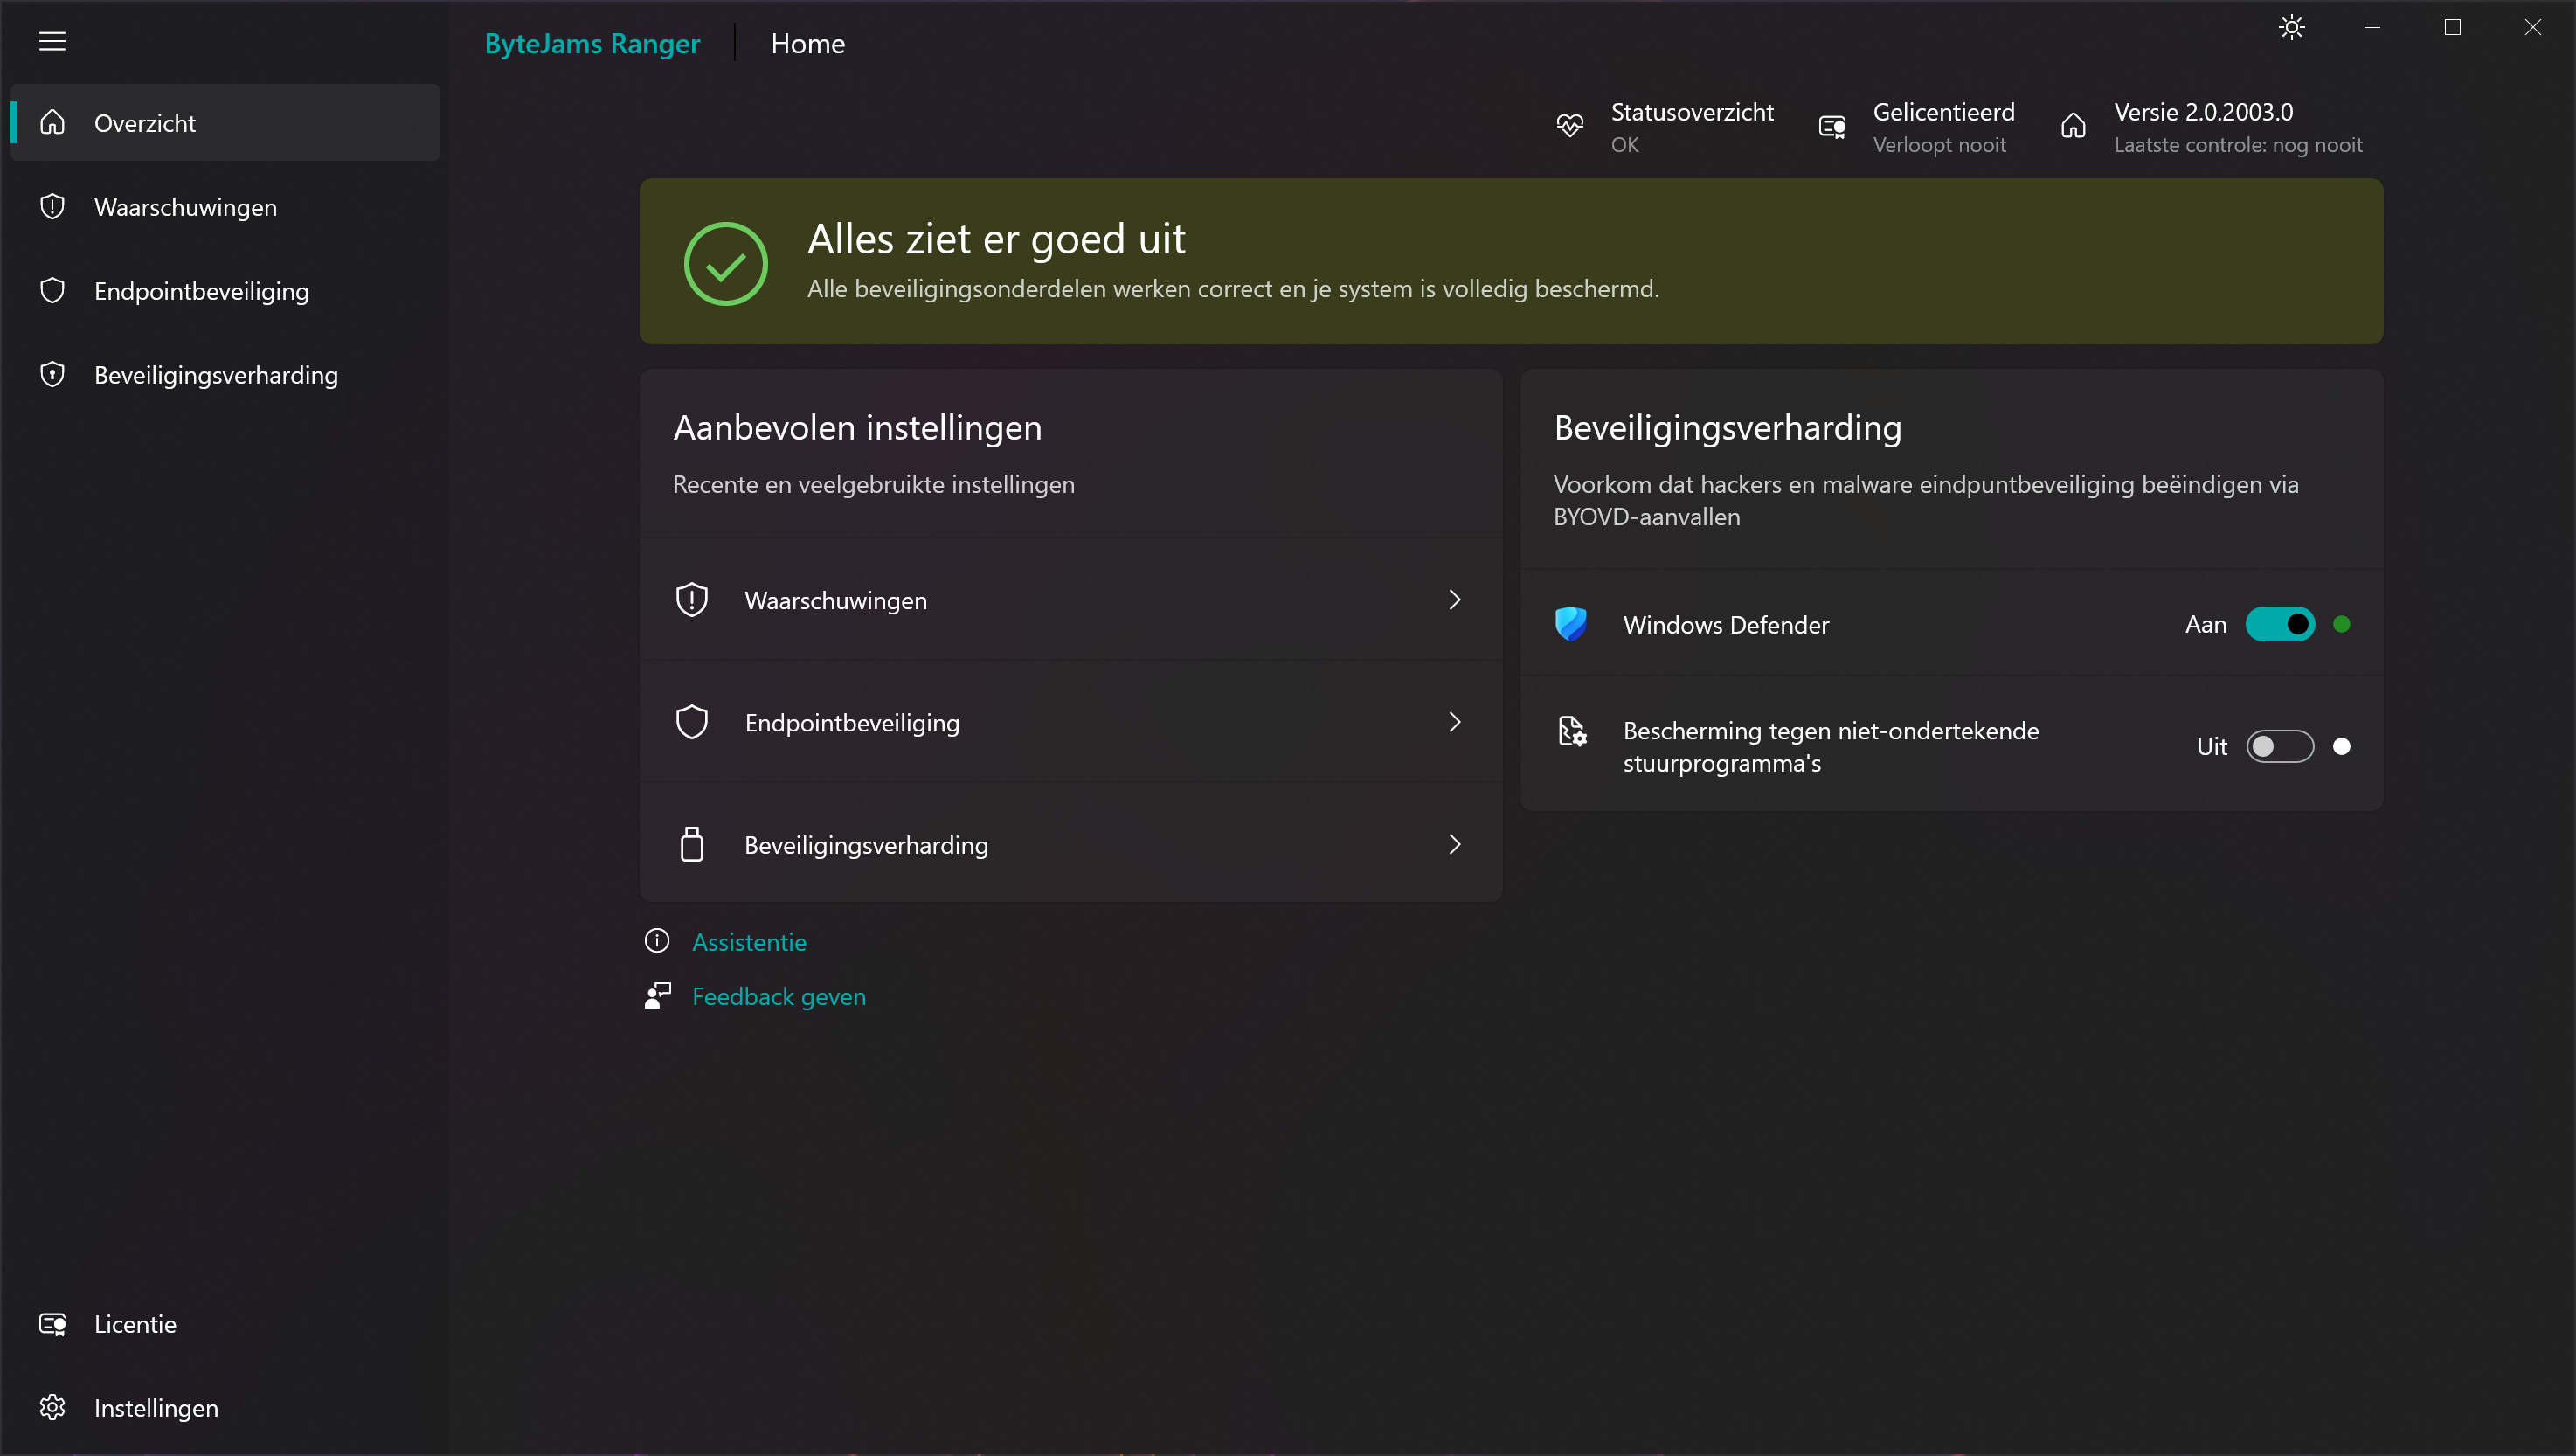
The kernel-free platform behind ByteJams Ranger: autonomous, on-device detection with no signatures, no cloud dependency, and no performance tradeoffs.
ByteJams Ranger showcases the future of endpoint protection: a kernel‑free solution that also blocks remote ransomware attacks, a persistent blind spot even for Gartner Magic Quadrant leaders.
While AI‑driven platforms promise adaptability, they are routinely bypassed. Attackers shape malicious code to look statistically benign and evade detection.
Our patented technology detects threats generically, without signatures, cloud dependency, or connectivity, making it ideal for air‑gapped environments.
We eliminate kernel components entirely, avoiding the system instability behind incidents like the CrowdStrike global outage.
While Microsoft is building its Windows Resilient Security Platform, ByteJams delivers protection today that addresses the root cause of 90% of successful ransomware breaches without compromising system reliability.
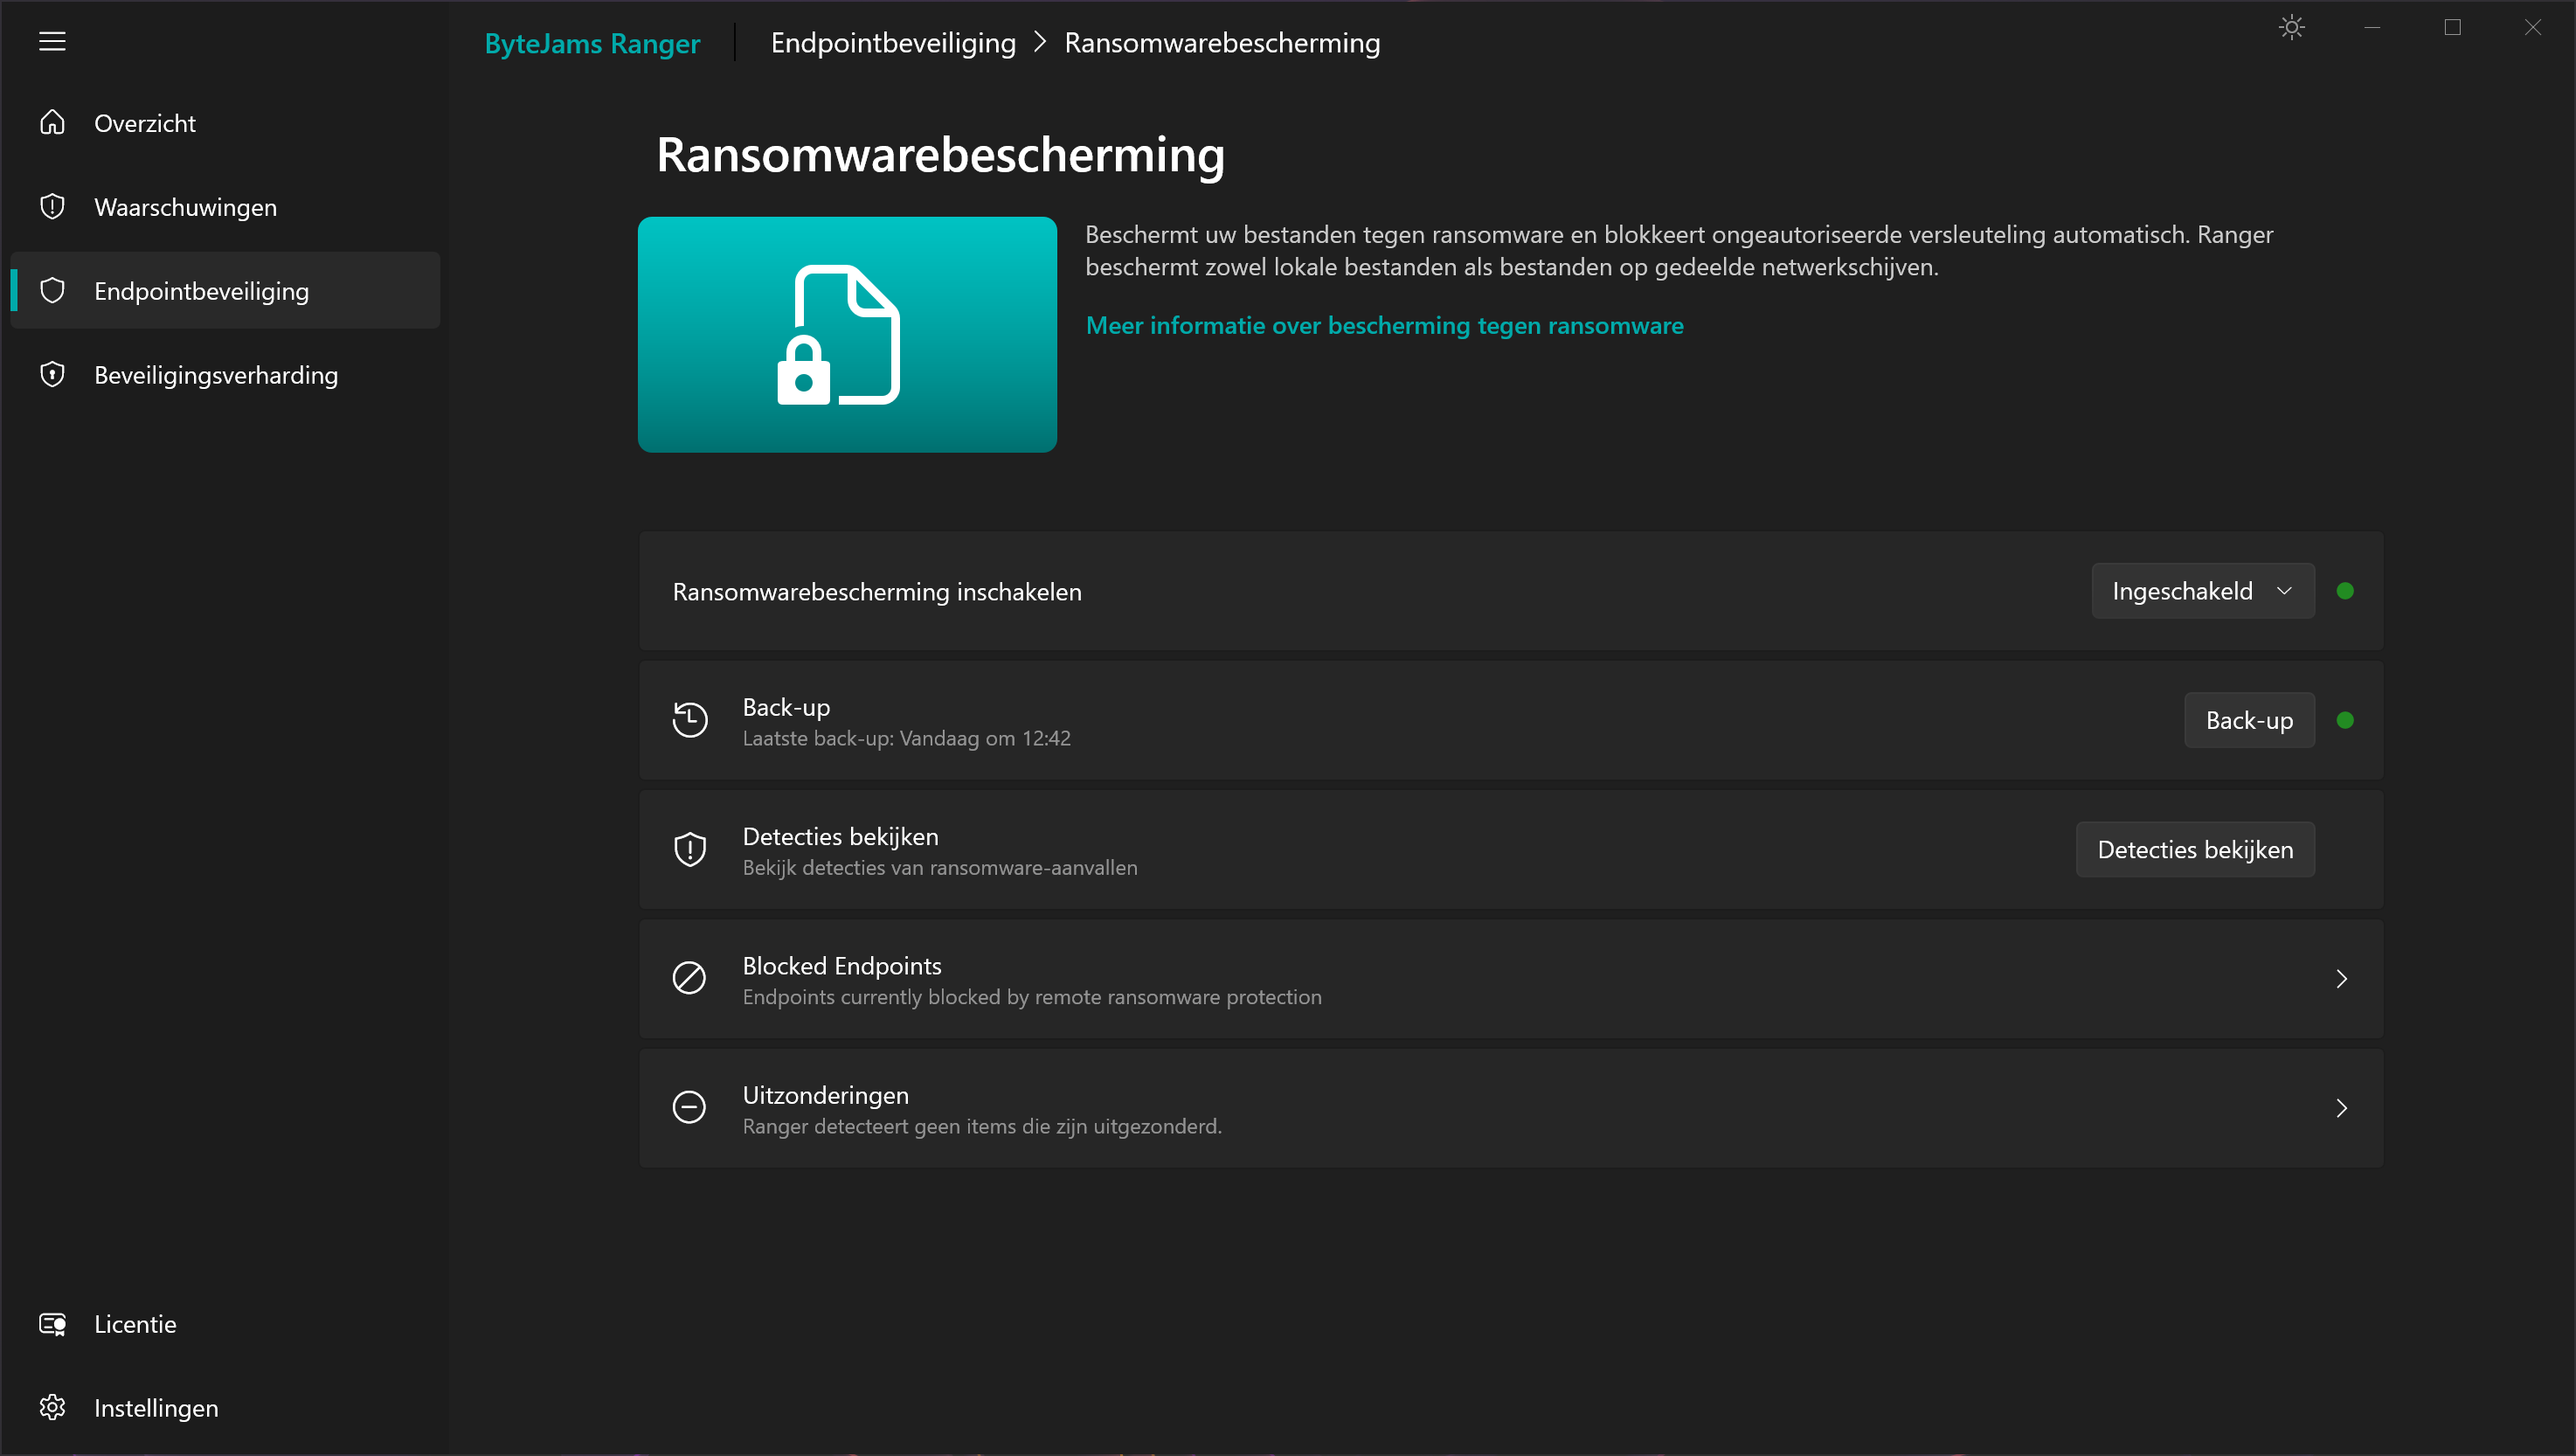
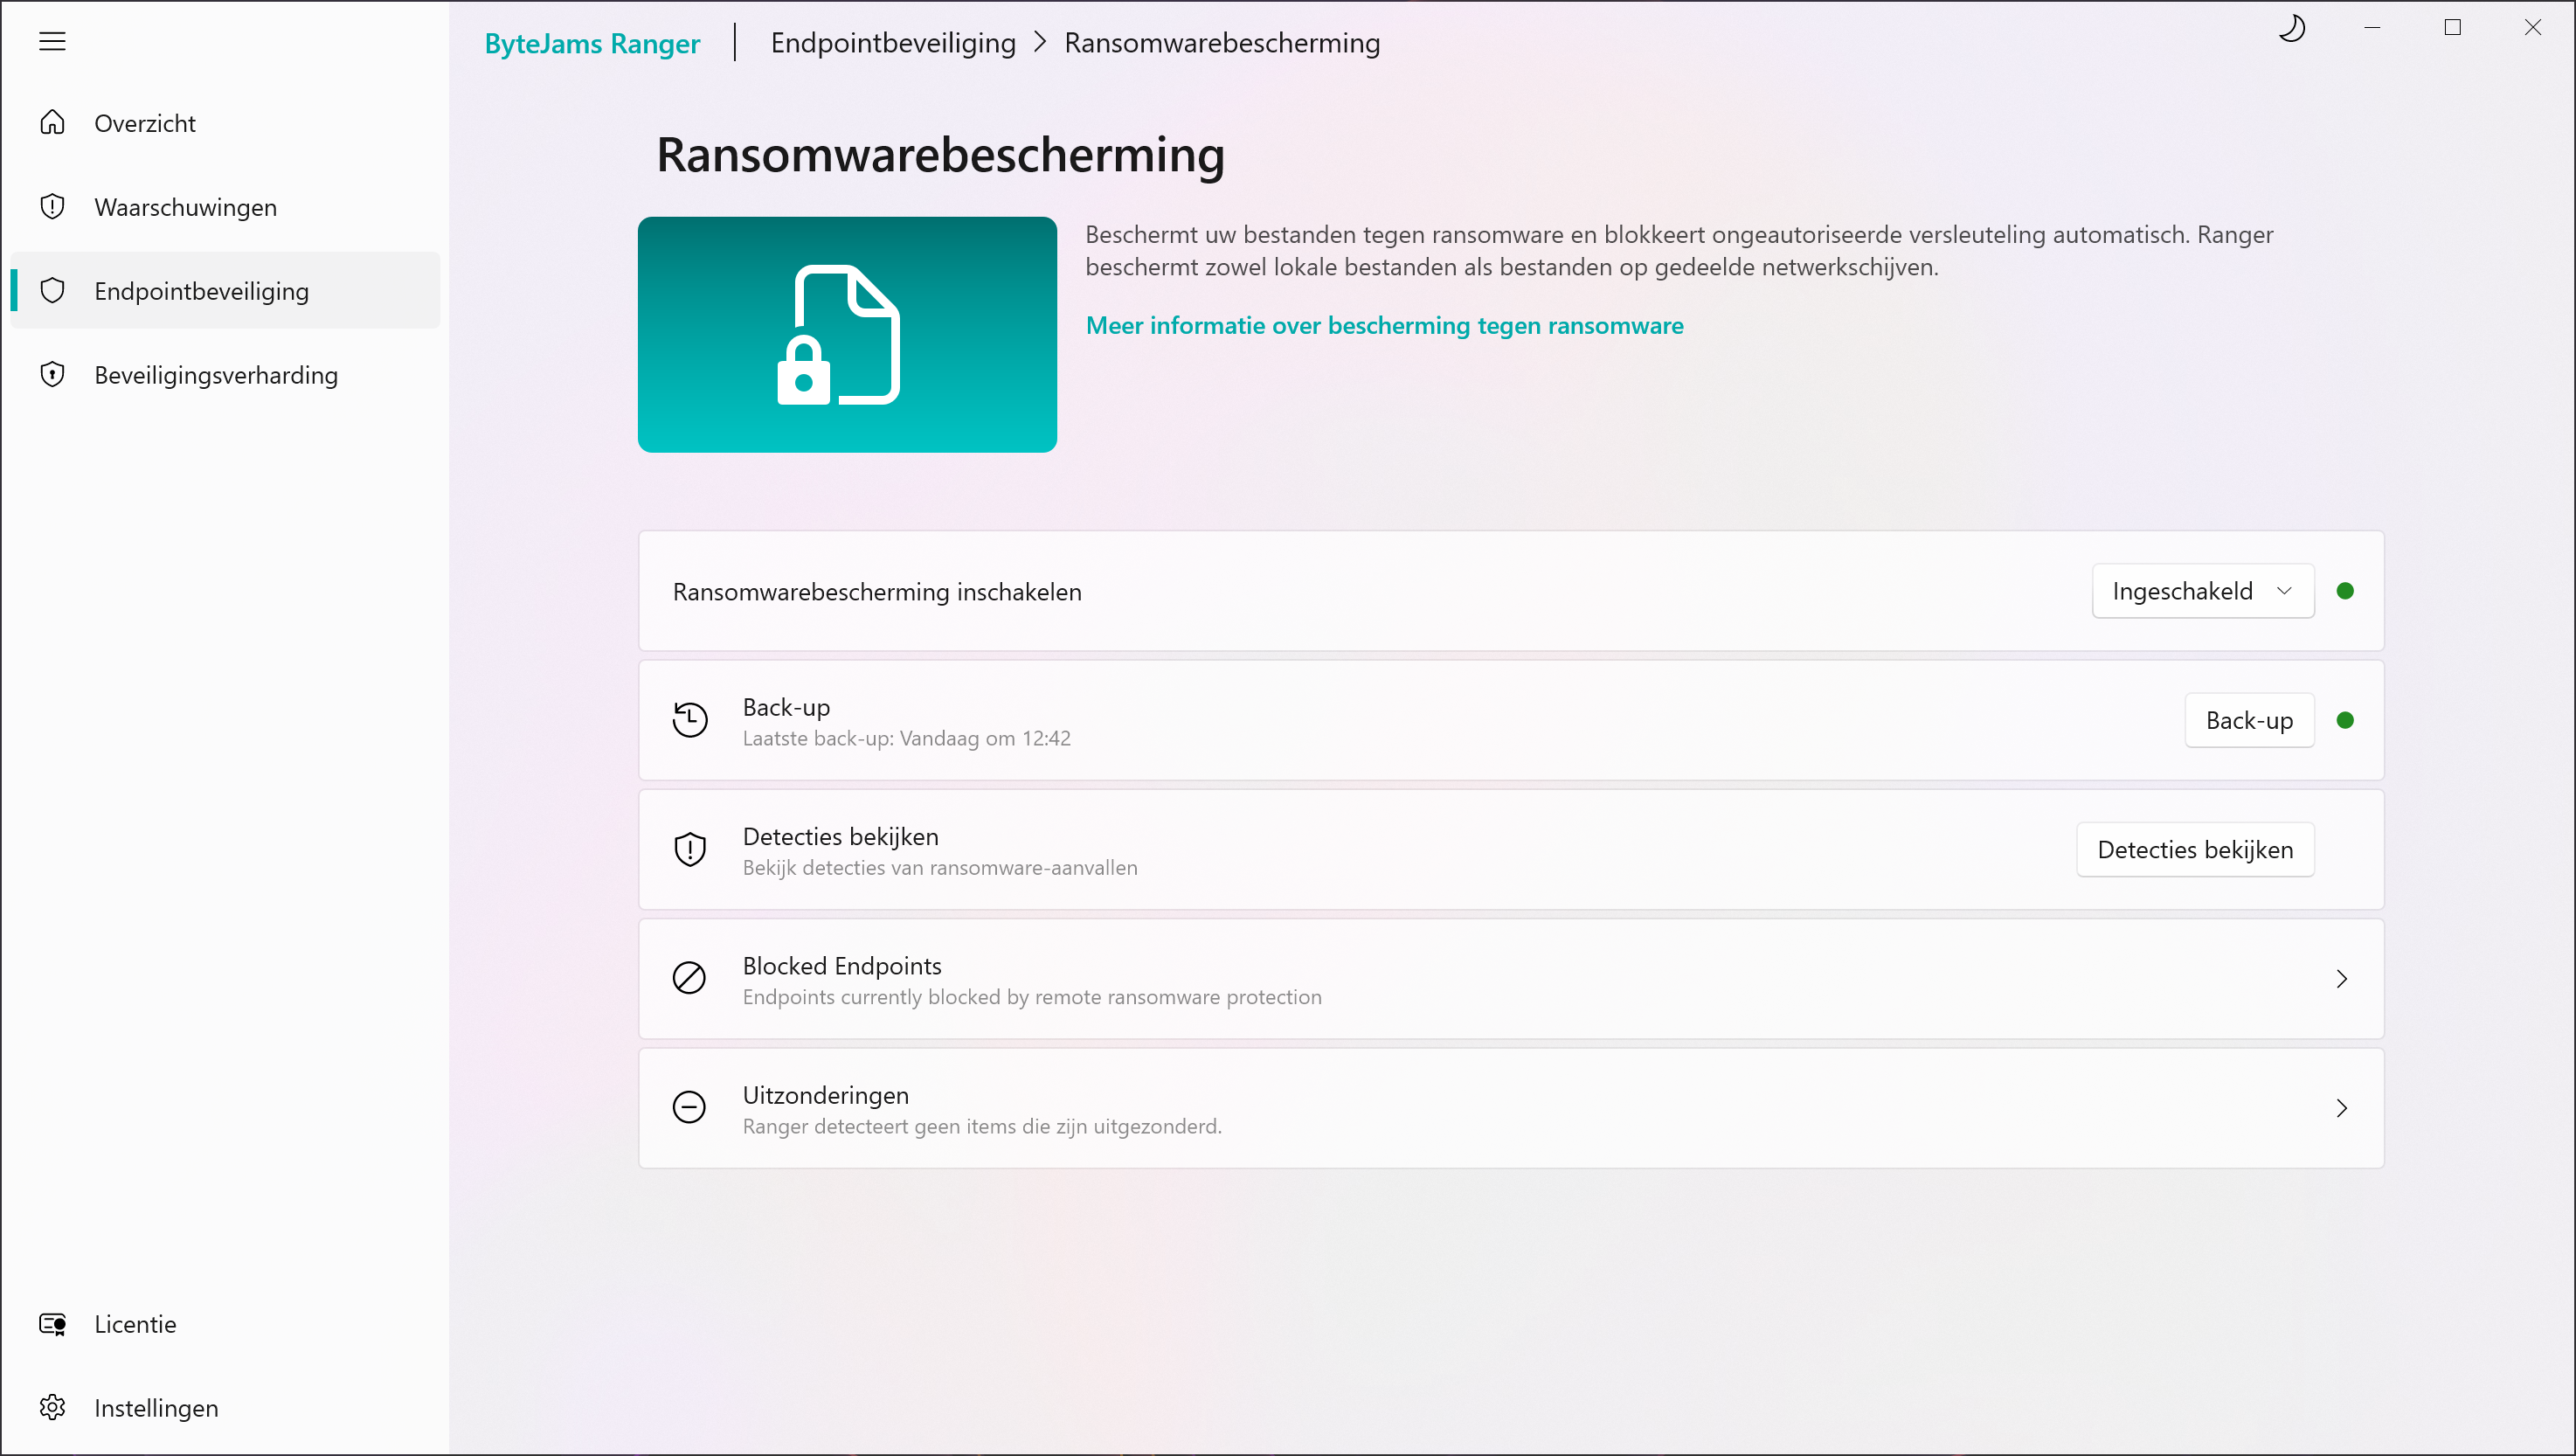
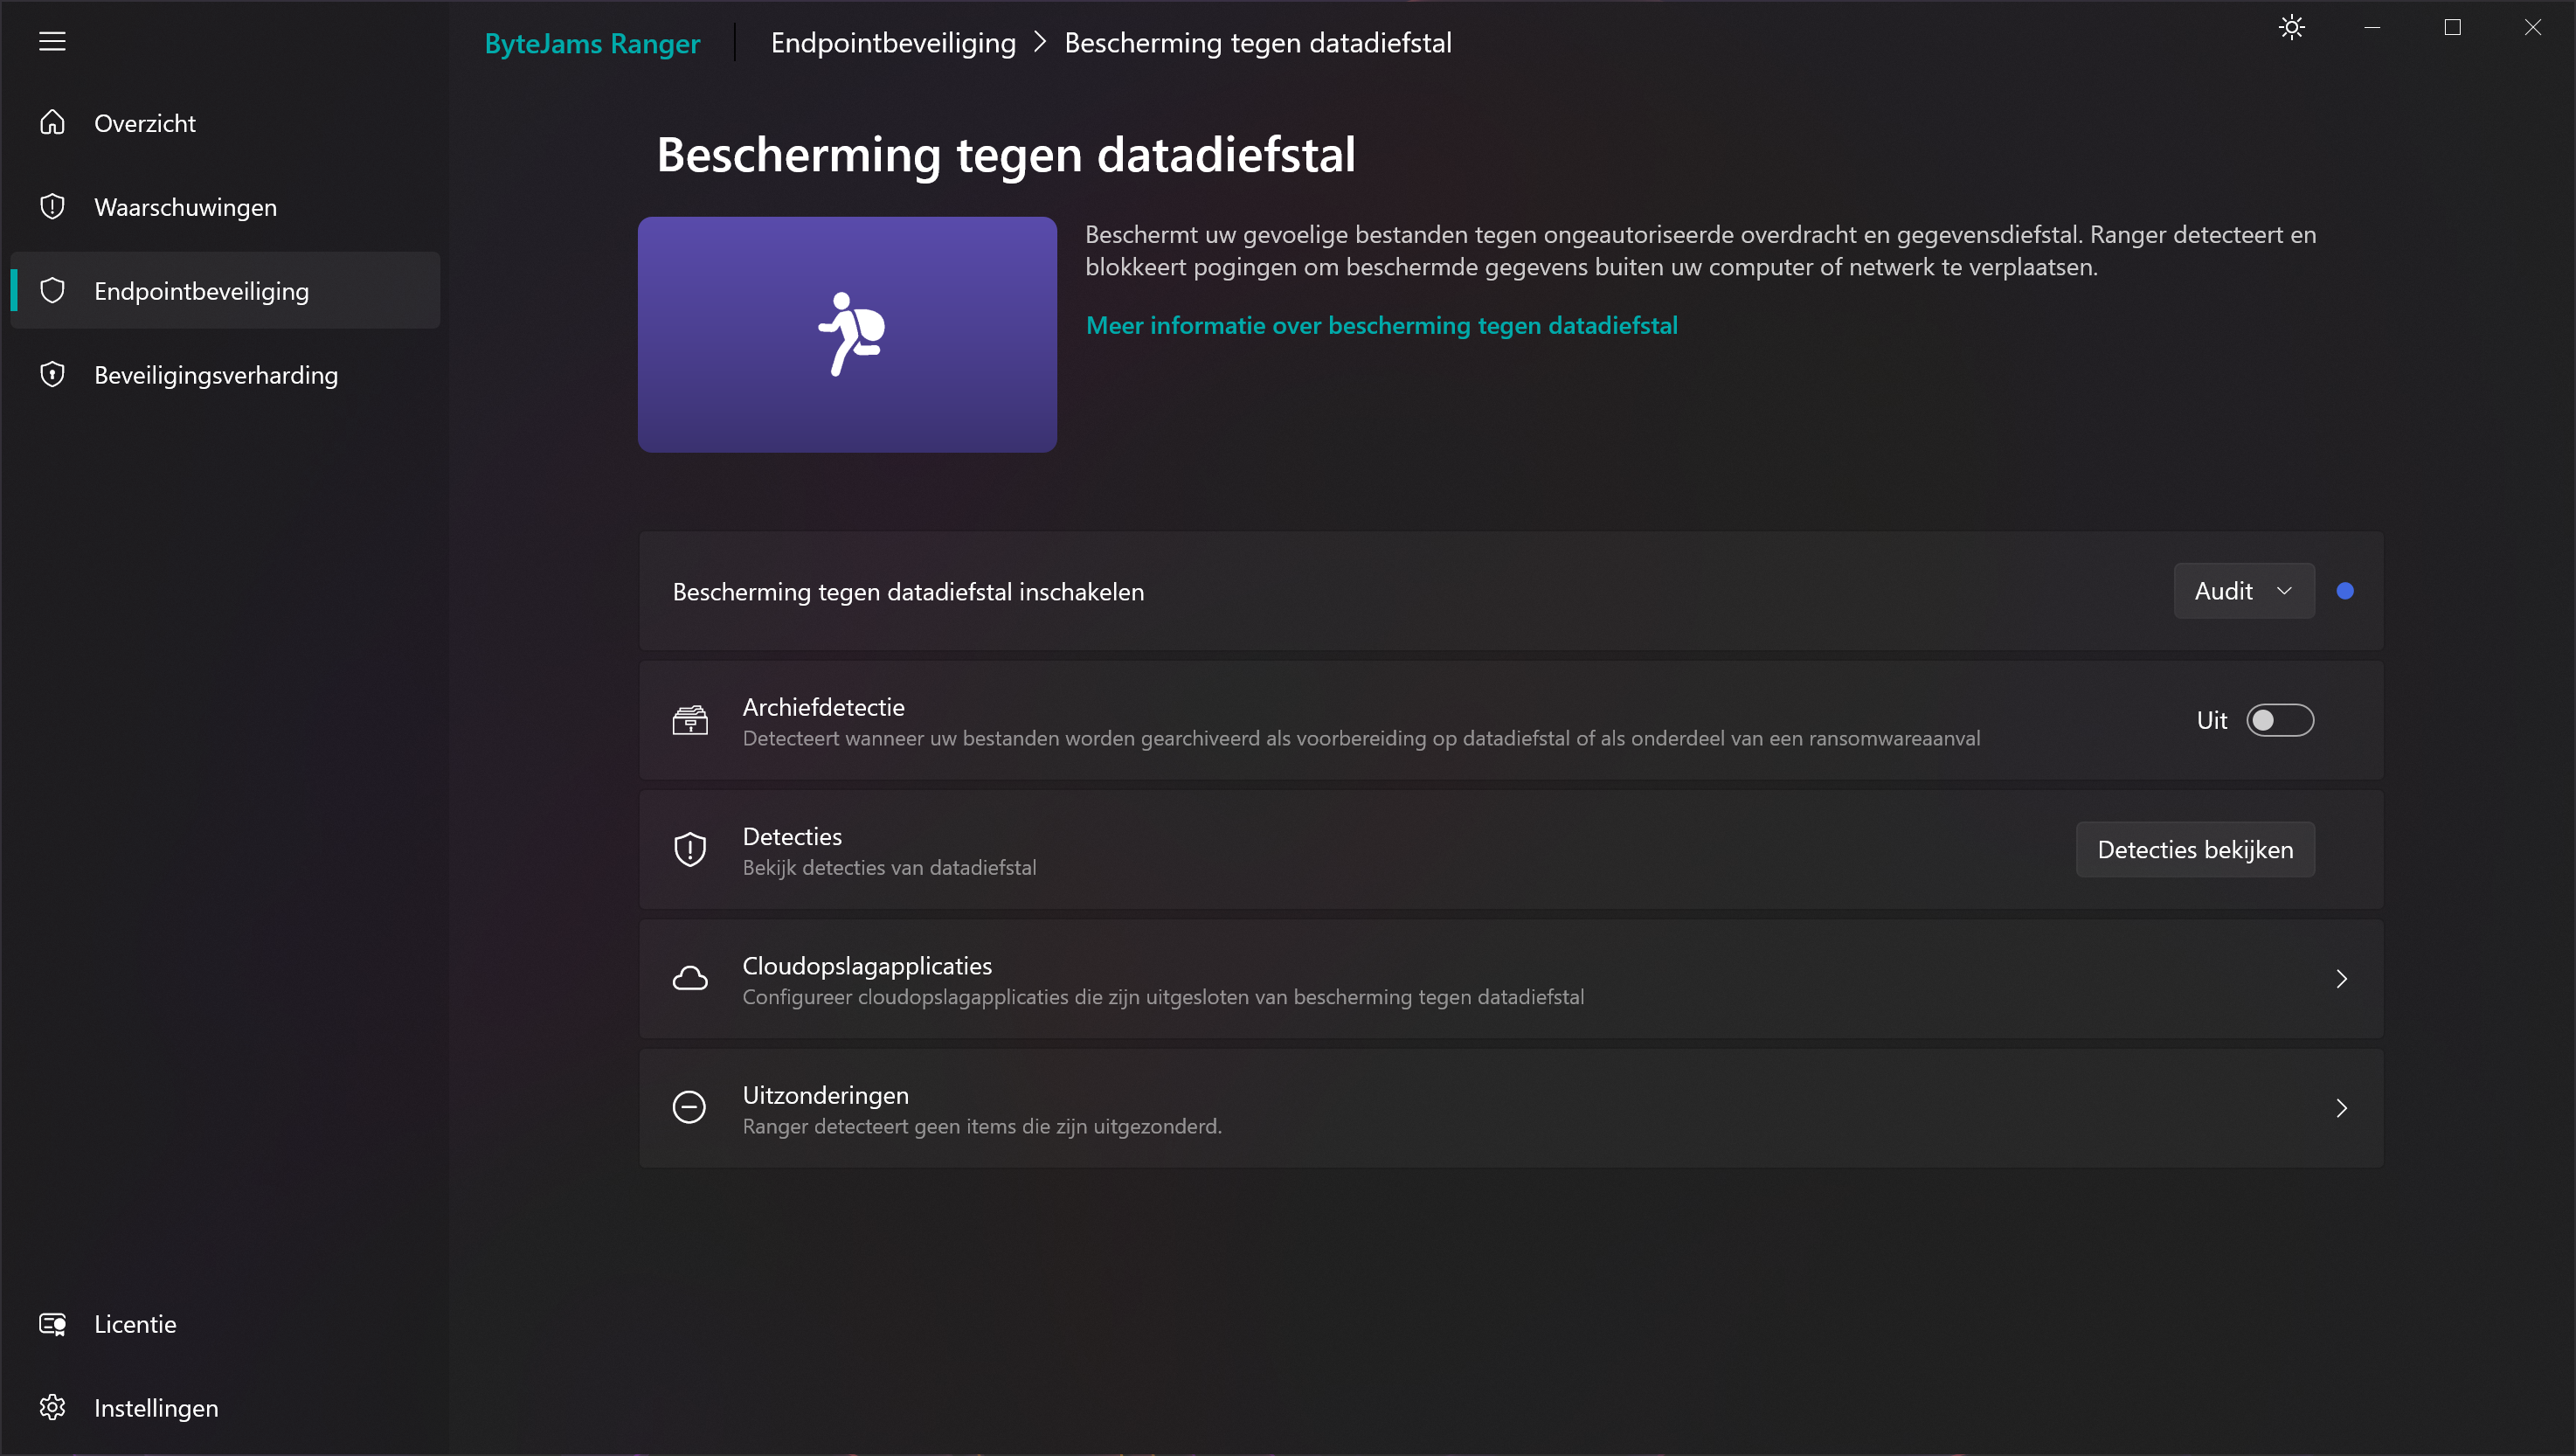
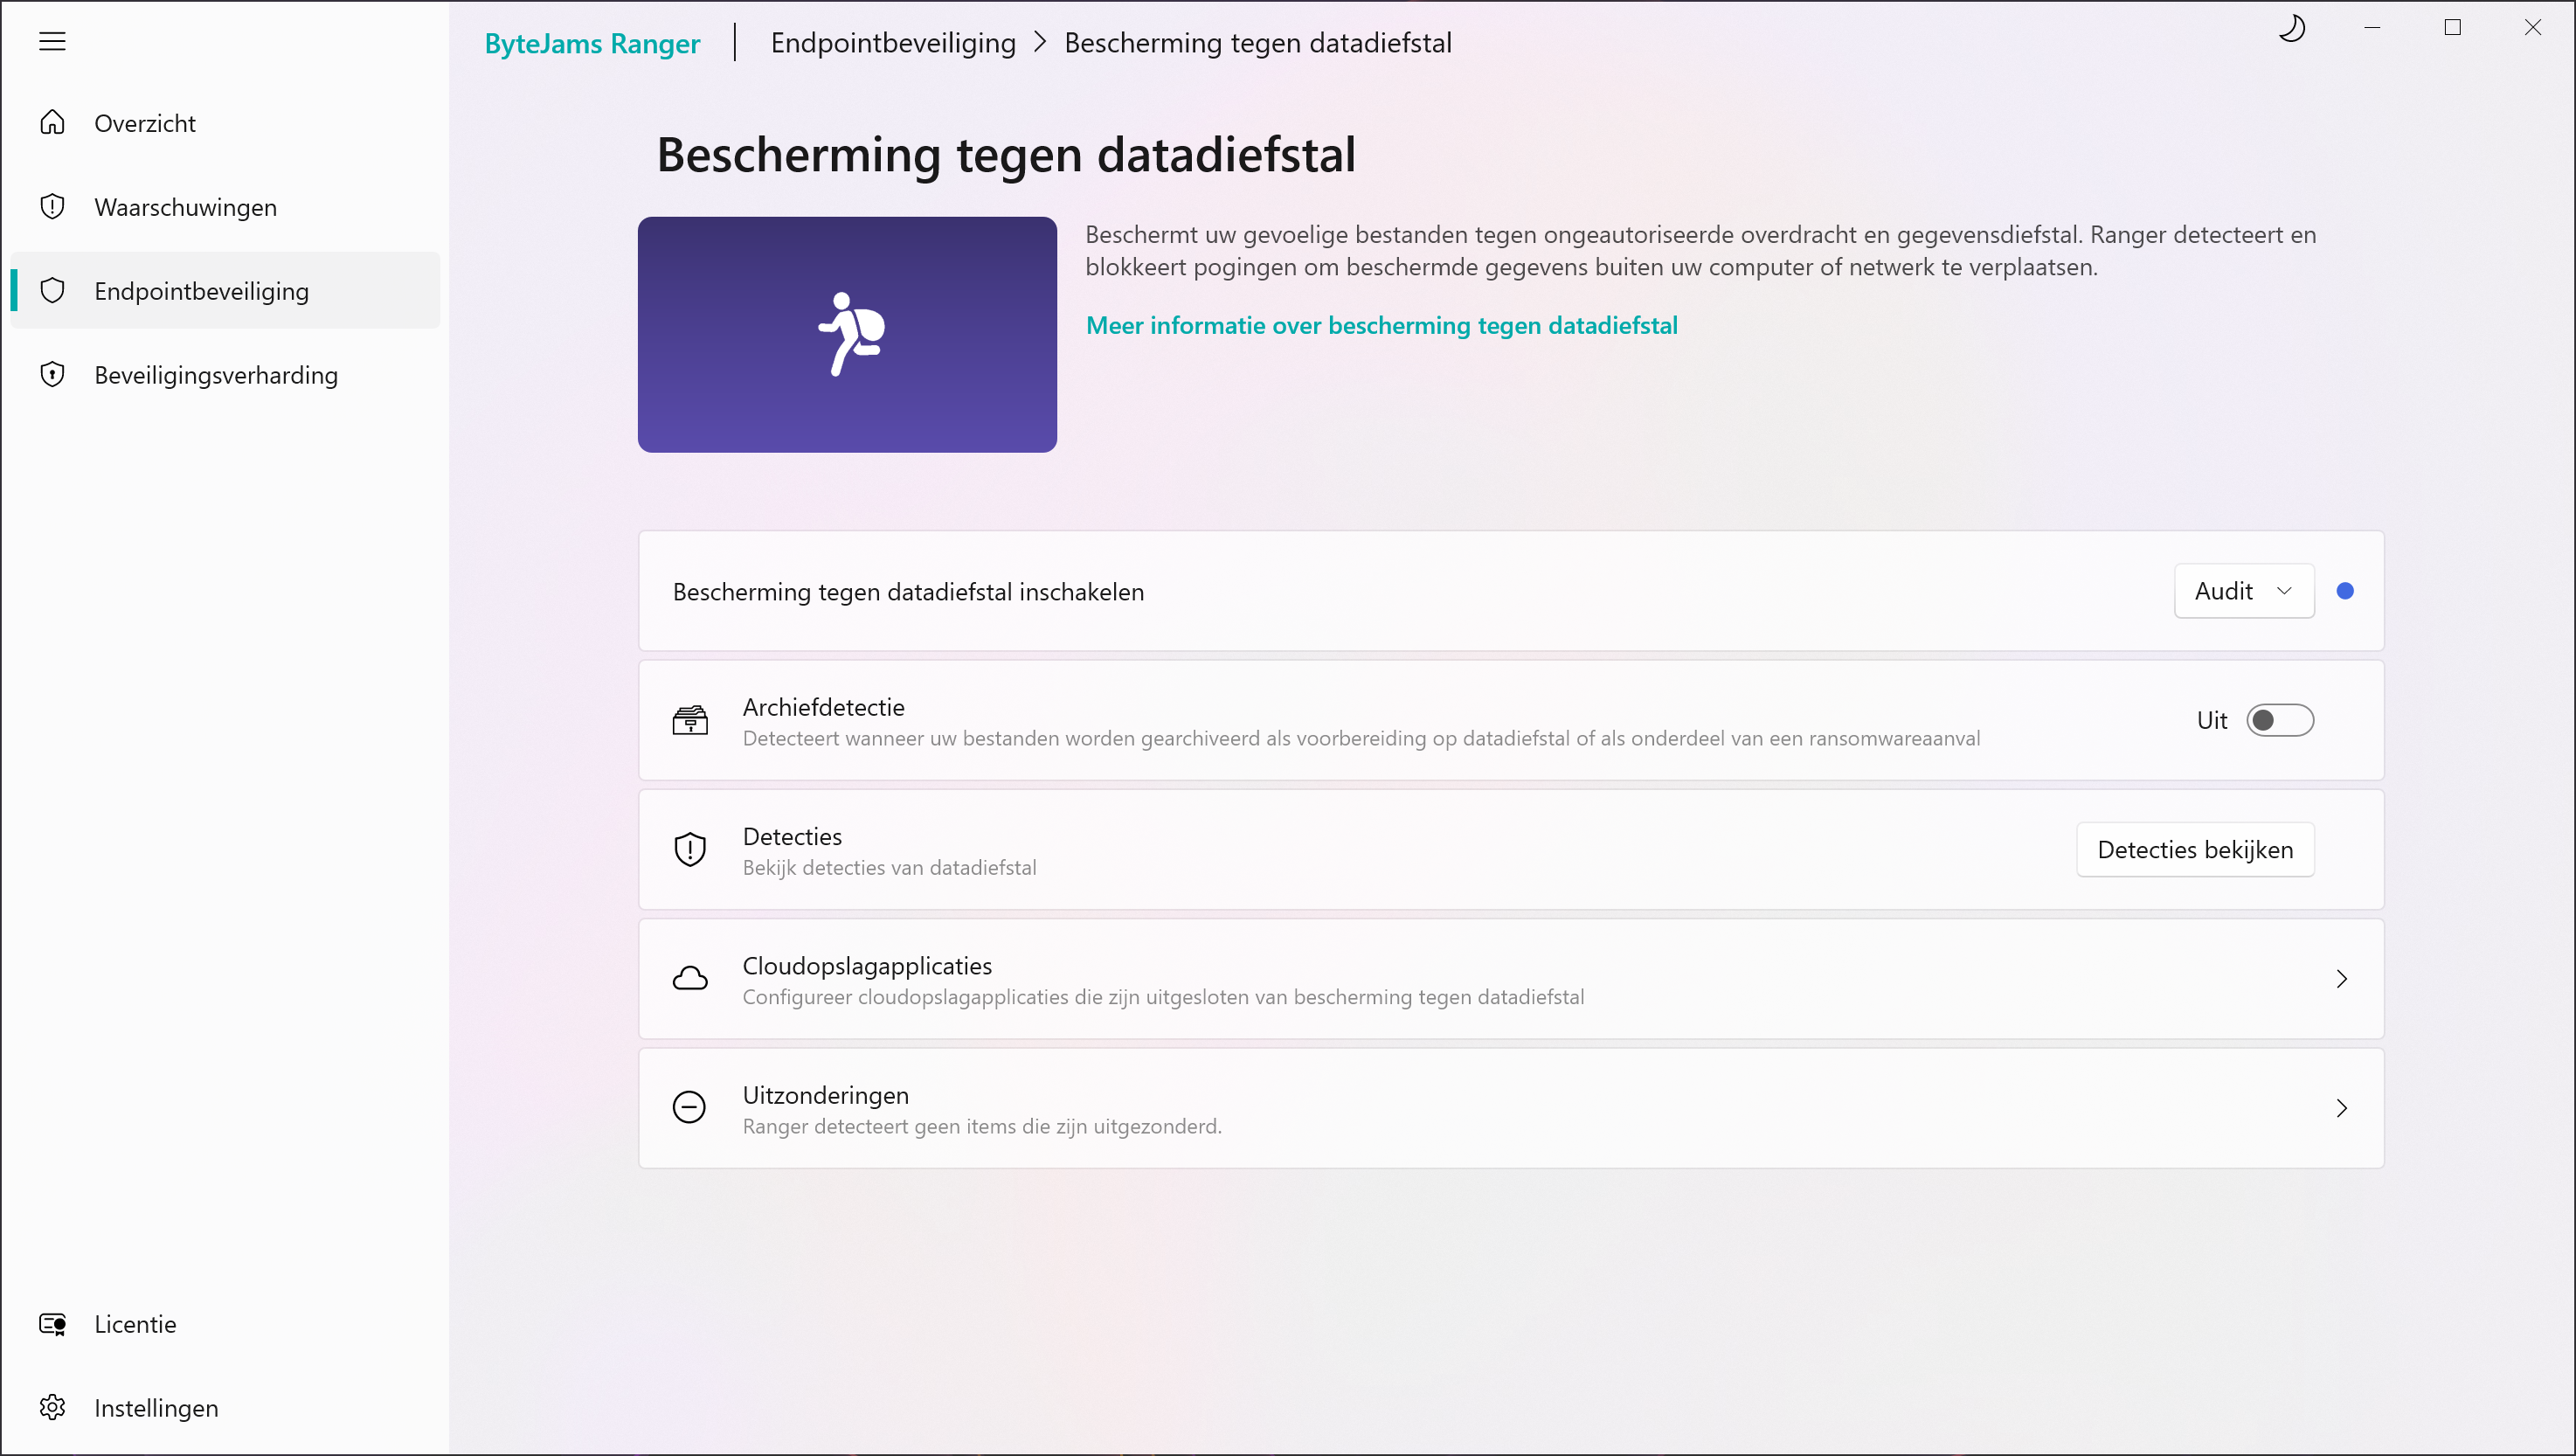
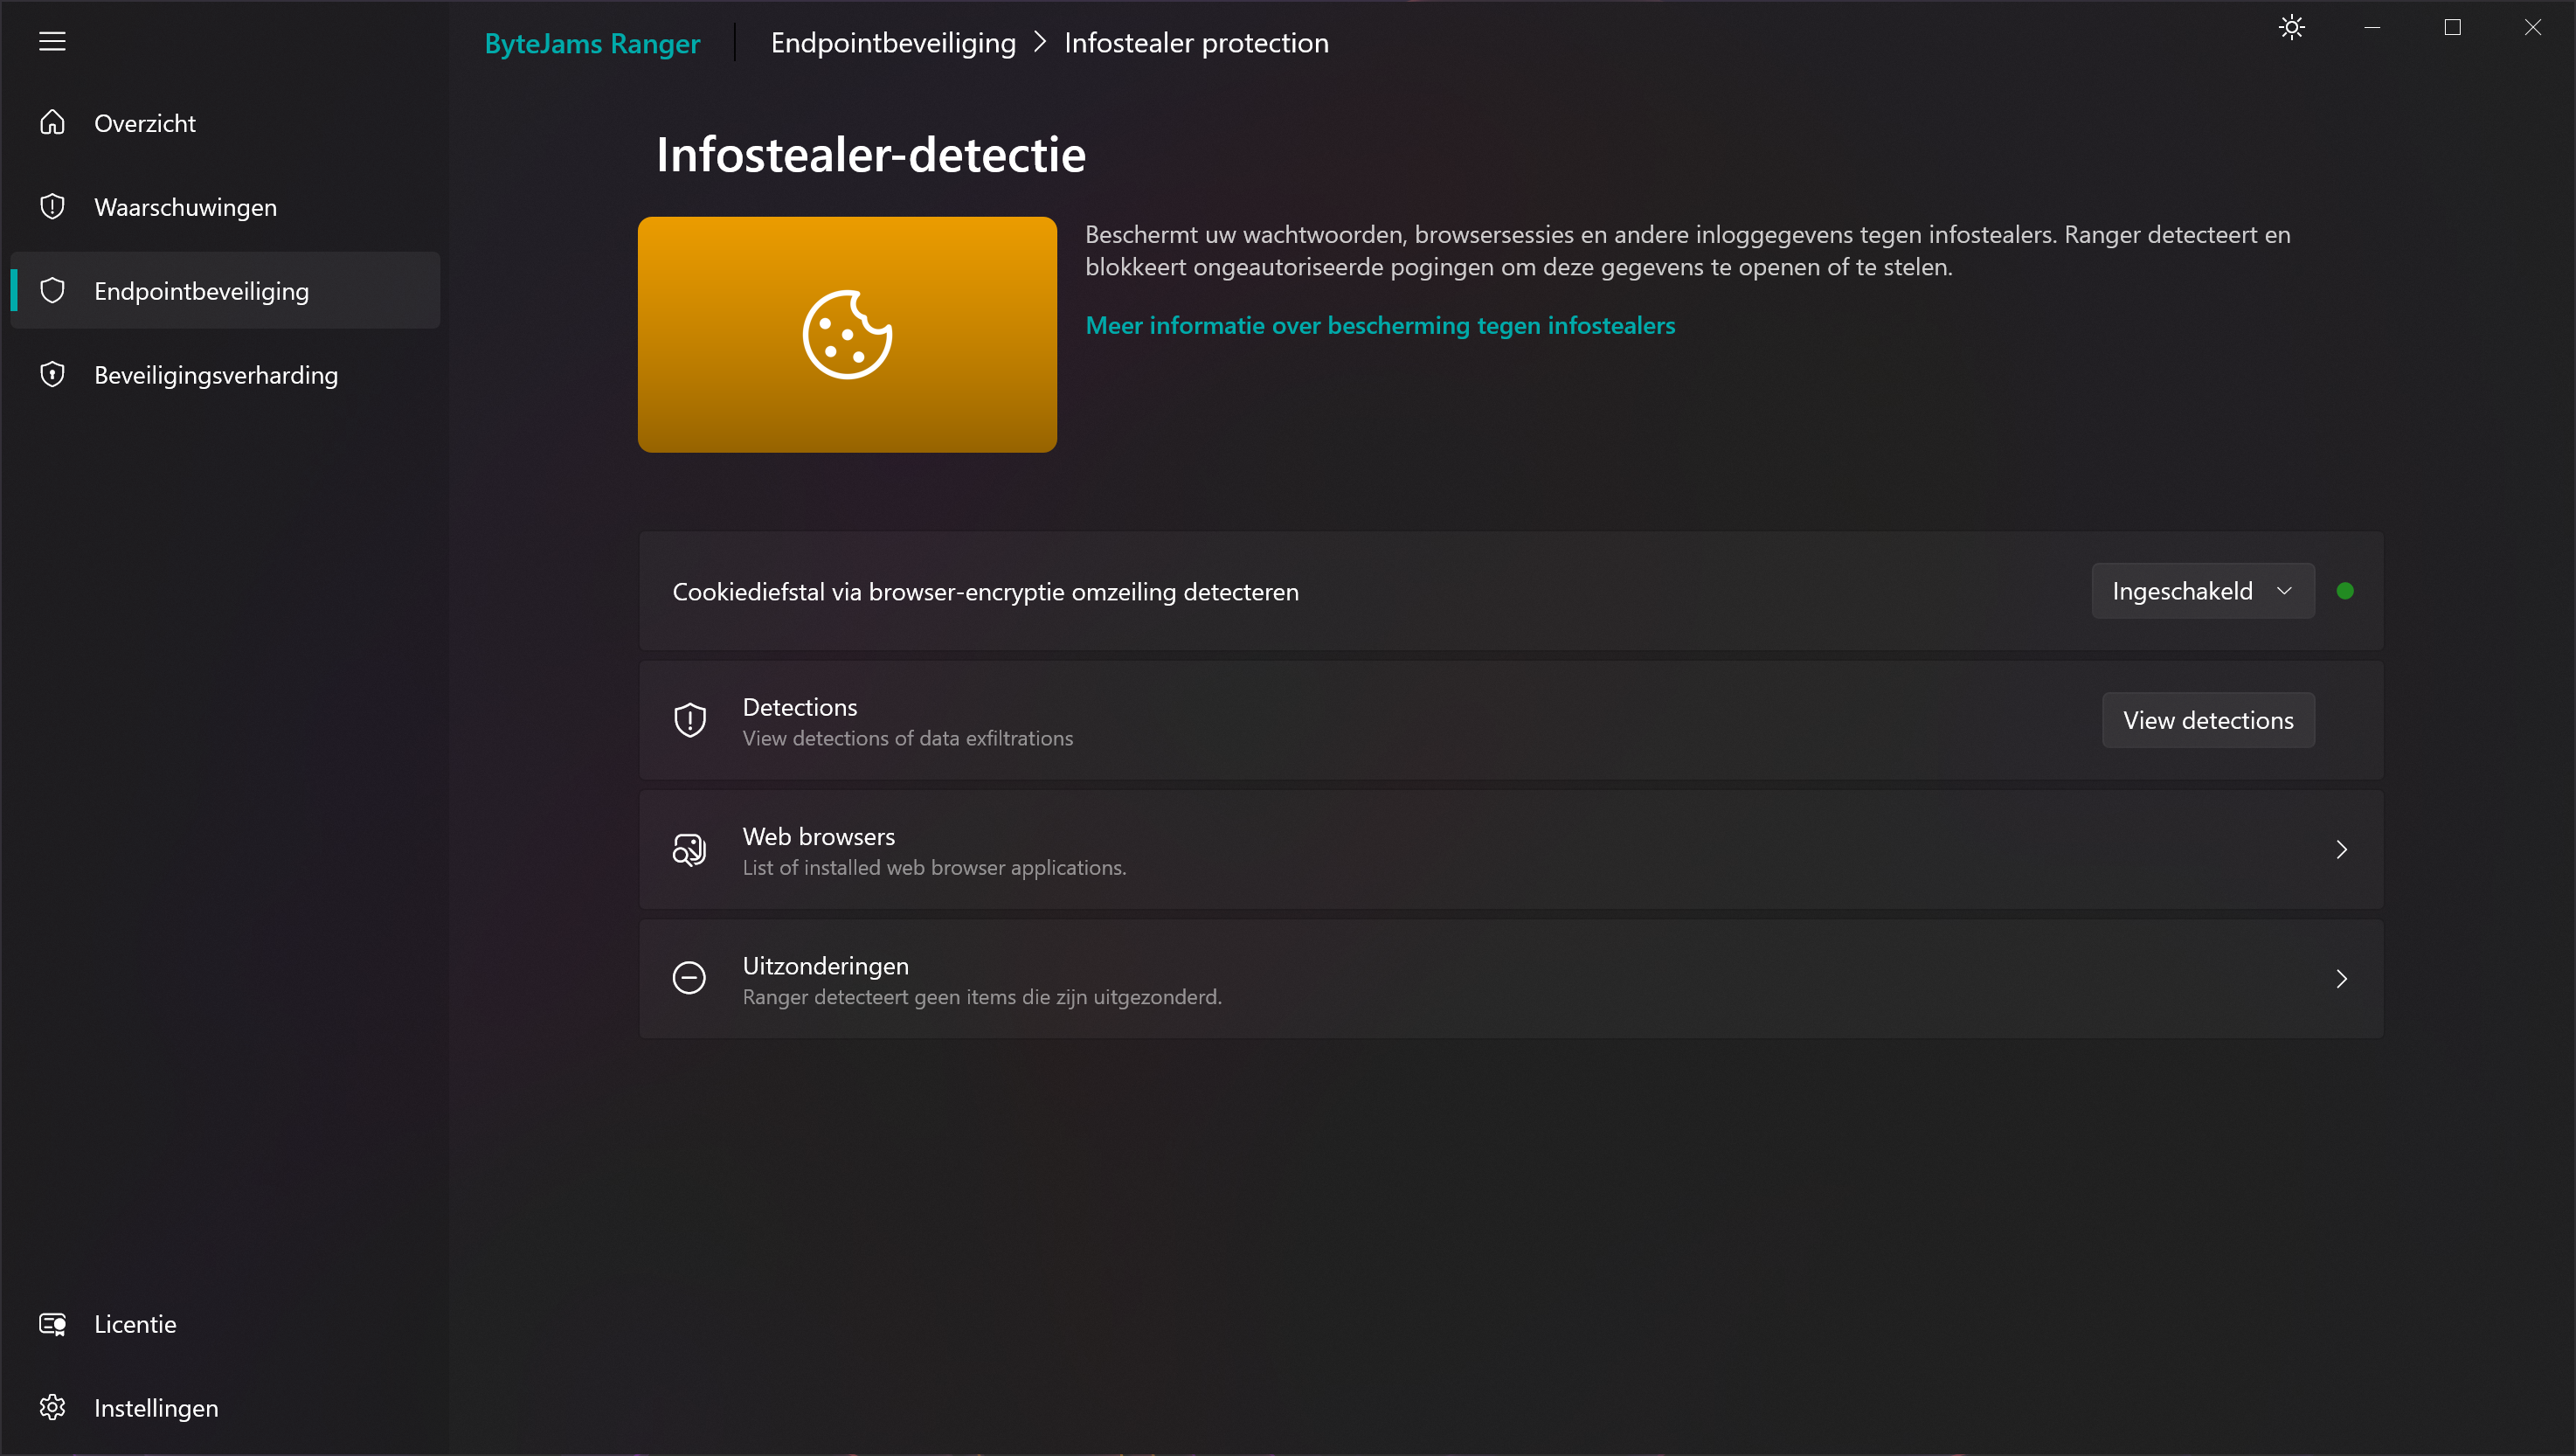
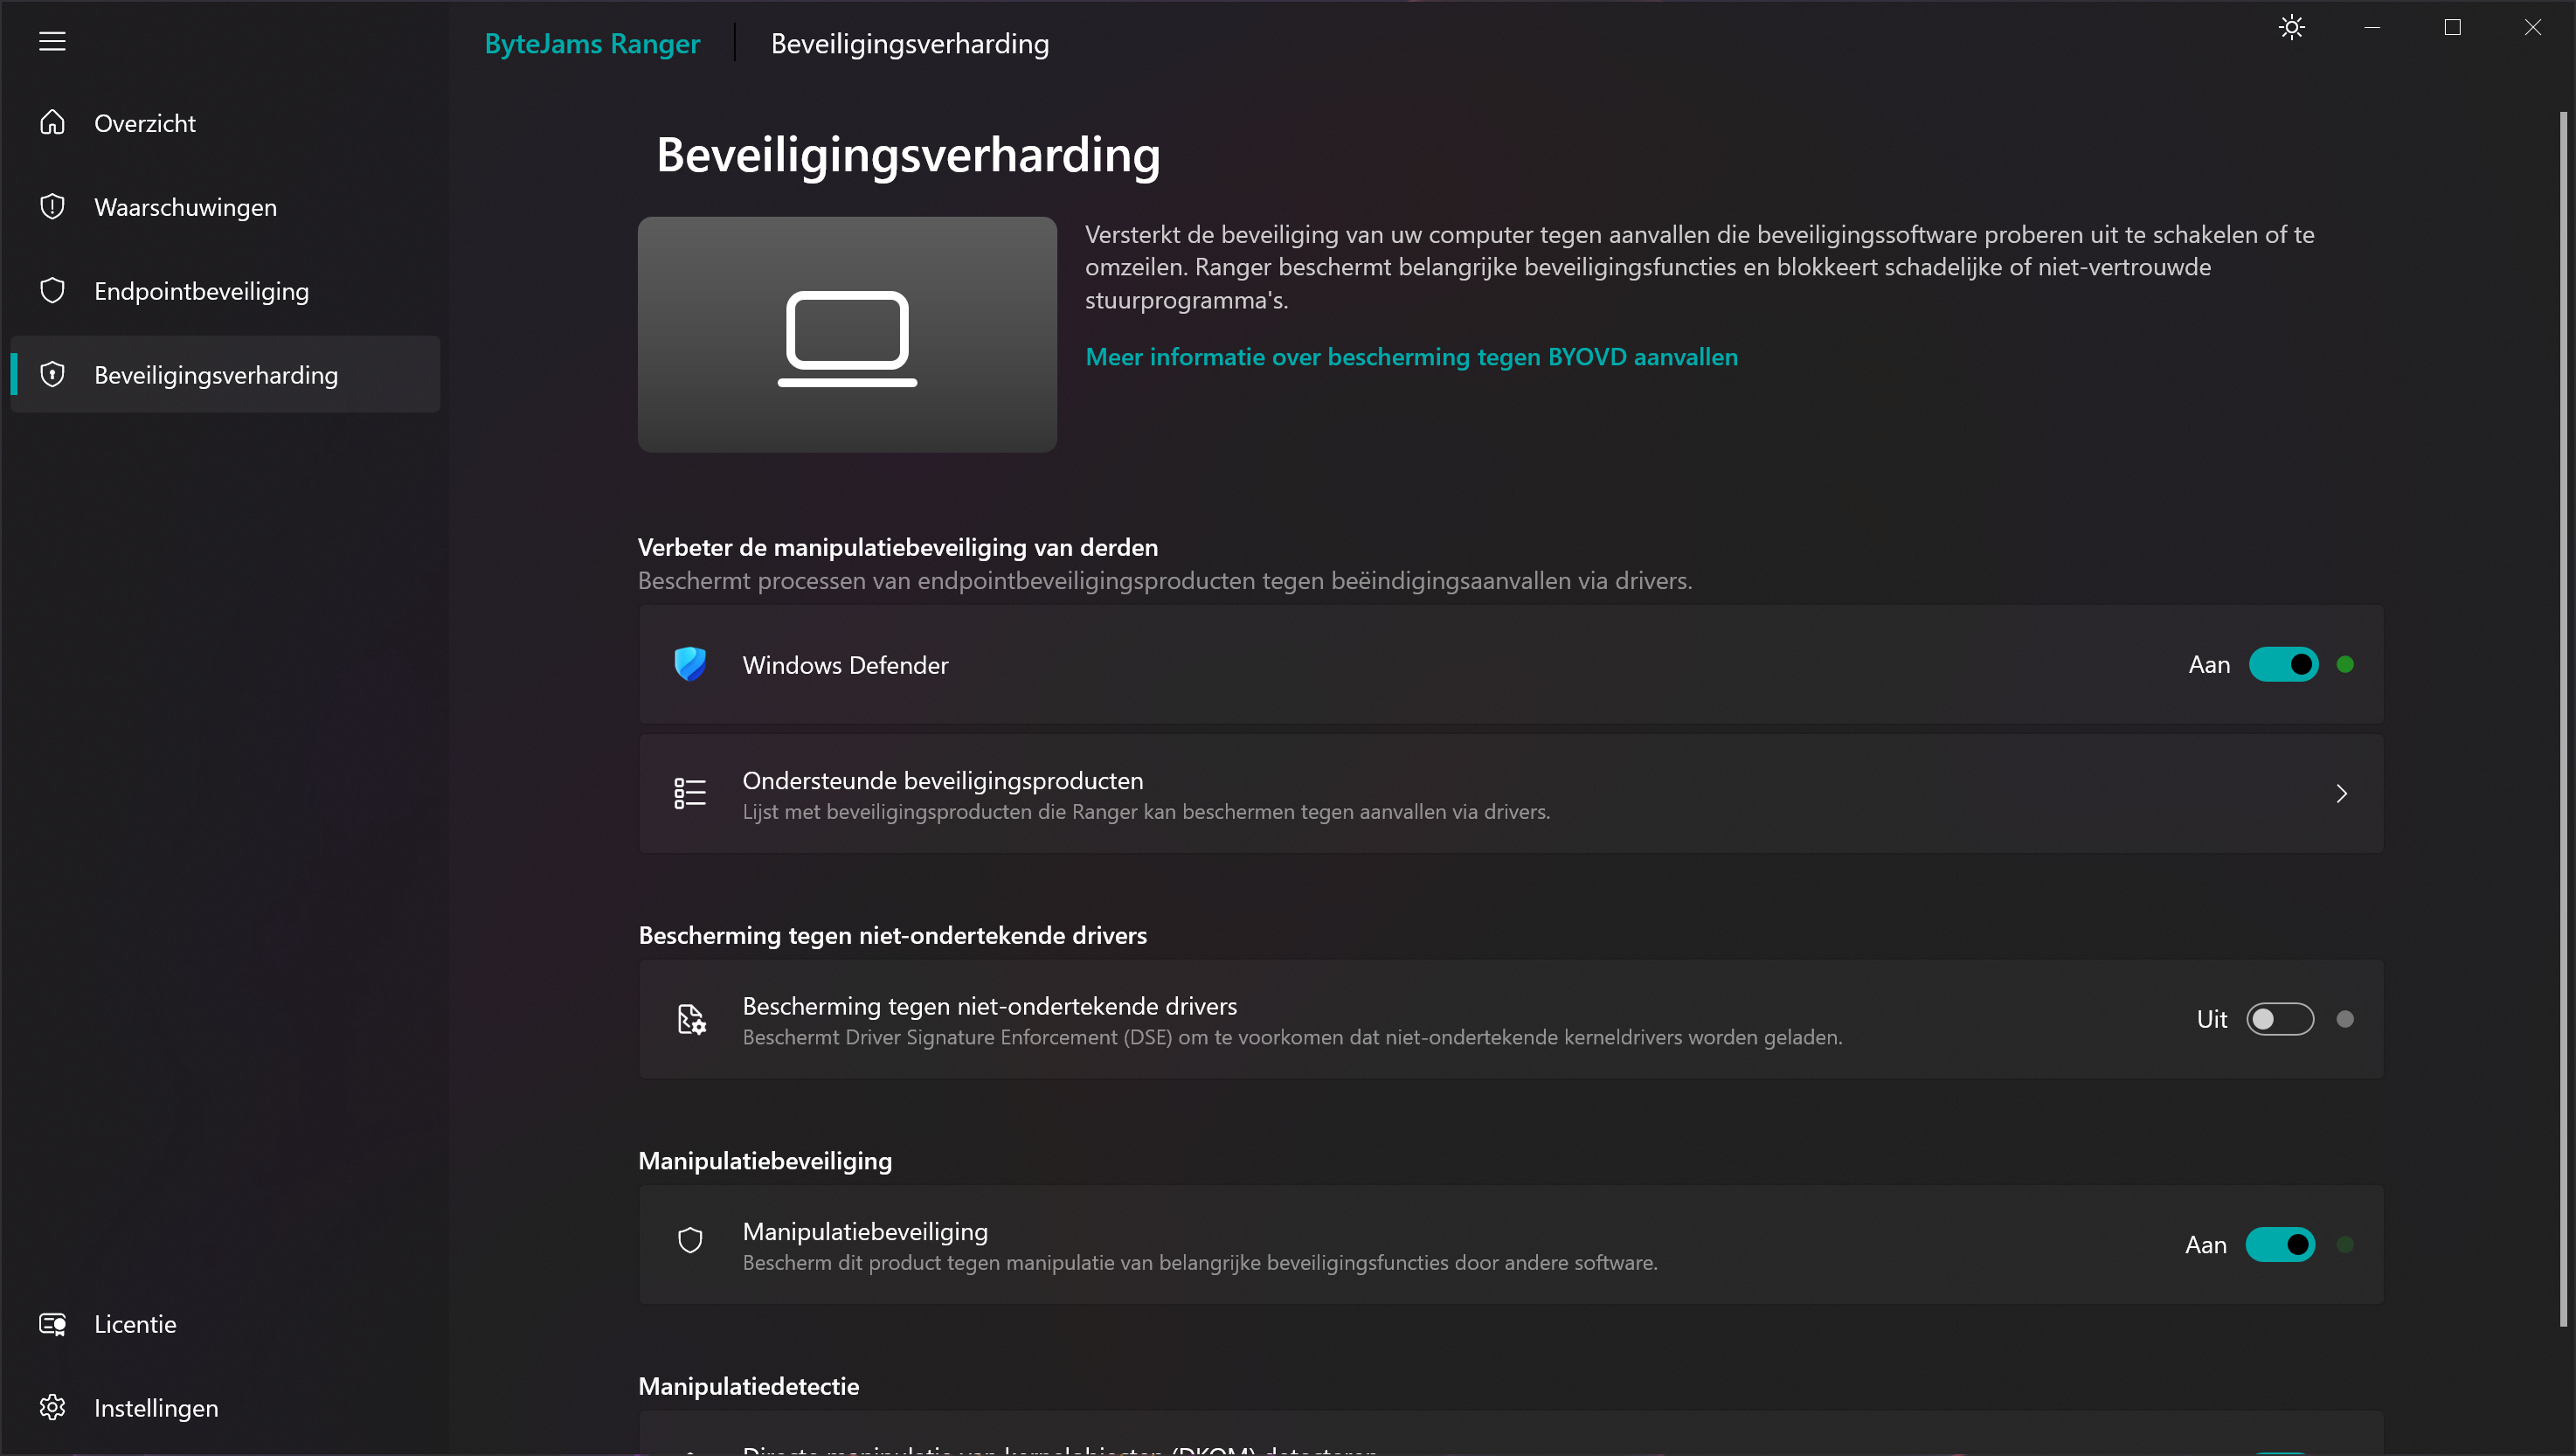
ByteJams Ranger is the first solution to natively produce high-fidelity telemetry fully aligned with the OCSF standard, making it compatible with, and enriching, existing telemetry pipelines.
Ranger protects critical assets from threats like ransomware and data exfiltration, making it an ideal sensor for Managed Service Providers (MSPs), Security Operations Centers (SOCs), in-house threat response teams, and Managed Detection and Response (MDR) providers. The platform delivers standardized, enterprise-grade endpoint visibility with minimal deployment and operational friction.
ByteJams is a contributor to the Open Cybersecurity Schema Framework.
© ByteJams B.V. 2026, all rights reserved
Made in The Netherlands